Vulnerability Management in Communications: Why Service Providers Need to Look Beyond CVSS
Read More
 Communication Service Providers Build a strong foundation with Network transformation
 Hitech Transform hi-tech operations with digital innovation
 Travel & Hospitality Enhance guest experience with technology
 Retail Hyper-personalize retail customer experience
 Public Sector Harness power of digital in Public Sector


AI agent security is the practice of protecting autonomous AI systems through a combination of governance, technical guardrails, and continuous risk management. As enterprises deploy AI agents that access sensitive databases, APIs, and multi-agent ecosystems, the attack surface expands beyond traditional applications. Key threats include prompt injection, excessive agency, tool abuse, memory poisoning, and credential compromise. A strong framework starts with governance models like the NIST AI Risk Management Framework (Govern, Map, Measure, Manage), then enforces guardrails such as identity-mapped least-privilege access, runtime policy enforcement, secure tool invocation, input-output filtering, human-in-the-loop controls, and sandboxing. Risk management should shift left, spanning design-time assessment, pre-deployment red teaming, and continuous observability. Ultimately, securing agentic AI is about building trust—the advantage goes to organizations deploying the most secure, governed, and observable agents, not simply most number of agents.
How can enterprises securely scale autonomous AI systems without compromising on trust and security compliance?
Executive leadership across the world has been looking for an answer to this question. From customer support and software development to IT Ops and supply chain. Agentic AI systems promise to transform the value chain delivery in all major facets of industries worldwide. The trend is clear, organizations are no longer looking to deploy AI just to answer questions and summarize documents. AI is now undertaking tasks carrying significantly higher security risks like interacting with sensitive databases, external tools and being a part of much larger multi agent ecosystems.
As organizations scale their AI agents, security can no longer be just an afterthought. Enterprises will need a comprehensive AI agent security framework that combines governance, technical guardrails and risk management practices.
Unlike traditional applications, AI systems interpret instructions dynamically and adapt based on context. This provides flexibility and automation at an entirely new level but it also expands the attack surface significantly.
For example, following are some of the top sources AI agents have access to today –
In effect, if you see organizations today are onboarding digital workers (AI agents) which operate probabilistically with privileged access to such critical systems. They can leak sensitive information, misuse enterprise tools or introduce cyberattacks at pace.
Agentic AI systems introduce several new risks across planning, reasoning, memory and tool execution. Attackers increasingly target these unique capabilities rather than simply exploiting software vulnerabilities. These new risks are significantly different from conventional applications and must be understood thoroughly. Many of these are covered in OWASP Top 10 Vulnerabilities for LLMs.
For example – a procurement agent reading some supplier document could unknowingly execute some hidden information that redirects payments or expose confidential information.
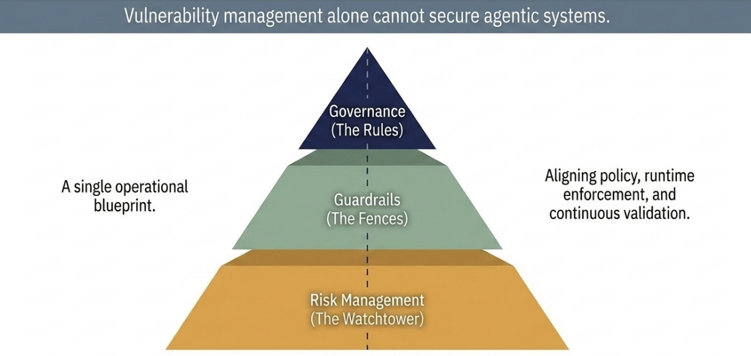
With the risk landscape laid out, enterprises are looking for measures to secure their agentic systems. Vulnerability management alone cannot secure AI agent security. Effective threat management begins with governance. The NIST AI Risk Management Framework (AI RMF) provides one of the strongest foundations for enterprise AI governance. It mainly does this by focussing on following four parameters –
Governance establishes what organizations expect AI agents to do and not do, whereas technical guardrails actually ensure AI agents operate within those set boundaries while in execution. There are few foundational ideas around which an enterprise can set up their guardrails.
As security controls and quality control activities are shifting left, same trend follows for Agentic AI deployments for enterprises. Risk management for agentic systems should start from design phase to ensure security while scaling.

Agentic AI is rapidly evolving from isolated assistants to interconnected Agent Foundries collaborating across enterprise workflows. The future AI agent security strategies are likely to focus on identity first least privilege enforcement, runtime policy engines and AI specific threat intelligence standards. These developments are engaging the entire industries into conversations to adopt global standards for AI agent Security. Evolving frameworks like NIST. OWASP top 10 for LLMs and ISO/IEC 42001 AI management system are moving the industry towards interoperable and secure autonomous systems. Ultimately securing agentic systems is not just about preventing cyberattacks but it is about building trust. The future belongs not to organizations deploying the most AI agents but to those deploying most secure, governed and observable agentic AI systems.


The short answer: Enterprises are evaluating VMware alternatives because Broadcom’s move to subscription-only, per-core licensing...
Read More